News
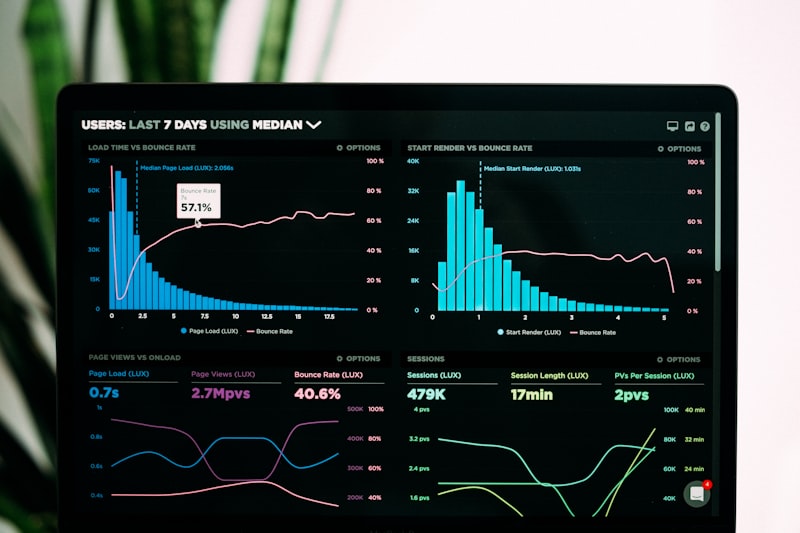
Fraud Detection That Doesn't Freeze Legitimate Accounts
How real-time monitoring paired with human review catches account takeover without the false positives that erode customer trust.
We replace legacy banking infrastructure with cloud-native platforms built alongside your compliance team, so modernization doesn't become the project your examiners flag next cycle.
Legacy core banking systems don't fail loudly. They fail slowly, in the form of a product launch that takes eighteen months because nobody wants to touch the system underneath it. We modernize the infrastructure without asking your compliance team to take that risk on faith.
We map the legacy system and the regulatory requirements around it together, so modernization starts from what actually has to hold up, not a generic migration checklist.
We replace outdated infrastructure with cloud-native platforms built for the compliance standards banking specifically requires, not general-purpose cloud architecture retrofitted after the fact.
Every migrated system passes a defined compliance review before it takes on live customer transactions, with a documented case your examiners can review.
We stay engaged post-migration, tuning fraud detection and compliance automation against real transaction volume instead of the assumptions made during design.

A digital banking platform built to compliance standards from day one means your next product launch doesn't stall in legal review for a system issue that should have been solved during design.
Strategic analysis, technical playbooks, and engineering updates shaping the future of banking.

Most legacy migrations don't fail on technology. They fail because compliance gets consulted after the architecture is already locked in.
How real-time monitoring paired with human review catches account takeover without the false positives that erode customer trust.
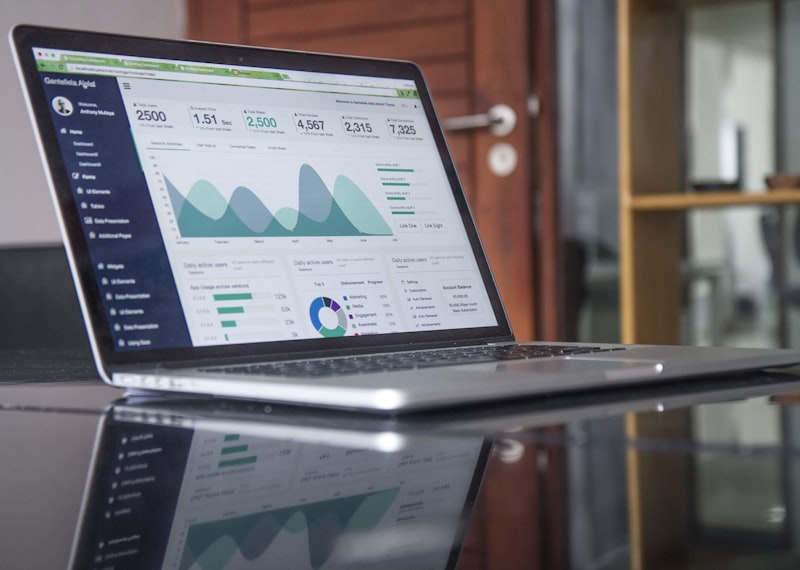
A practical look at building a compliance automation trail that holds up under regulatory review.
Why auditable risk models are becoming a competitive requirement, not just a nice-to-have.
Everything you need to know about FWC's banking technology, automation, and IT consulting solutions
We map regulatory requirements alongside the technical migration from day one, in the "Assess" stage of how we build, so compliance isn't a gate the project hits after the architecture is already locked in.
Every model routes ambiguous activity to a human reviewer instead of auto-freezing on a probability score, and we tune detection against your institution's actual transaction patterns rather than a generic fraud dataset.
Our risk models are built to be auditable, so your team can walk a regulator through why a decision was made, not just point at an output score.
Every migrated system passes a defined compliance review before it takes on live customer transactions, and we build a documented case your examiners can review rather than asking them to take the migration on faith.
We stay engaged post-migration, tuning fraud detection and compliance automation against real transaction volume, since the assumptions made during design rarely match year-one usage exactly.
Let’s turn business
challenges into opportunities.
Ask FWC AI anything
Instant keyboard navigation across all 15 services, 10 industries, 8 AI systems, and enterprise careers.